
Multiple Location Security
Secure Multiple Locations Without the Complexity
One cloud-managed platform. Zero Trust by default. Complete control over users, apps, and devices across all your sites: from office to remote work.
- 60% cost reduction
- 3 weeks to deploy
- 1 console for everything
The Multi-Location Security Challenge
Organizations with multiple sites face mounting security challenges.
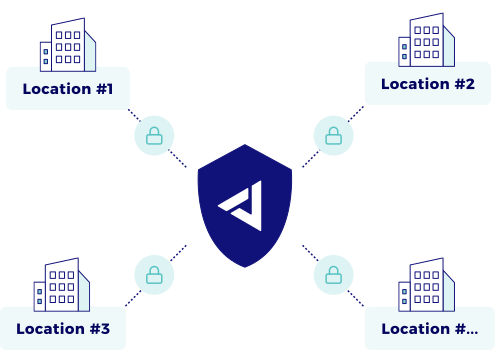
- Expensive firewalls at every site
- Slow VPNs frustrate remote users
- Once breached, attackers move freely between locations
- Limited visibility into who accesses what, where
- Security gaps between office, remote, and temporary sites
The result? Security complexity that grows faster than your business.
Deploy Fast
Virtual or physical controllers operational in hours. Most organizations secure all locations within 3 weeks.
Zero Trust Built In
Every user and device gets only the access they need. Compromised credentials can’t spread across sites.
Manage from Anywhere
One console controls policies, logging, and monitoring for every location. Changes deploy instantly.
Real SASE
for all your sites
Five Components, One Cybersecurity Platform
- ZTNA Network Isolation
Identity-based access to specific applications. Micro-segmentation keeps every user and device isolated. No broad VPN access.
- SD-WAN
Reliable, high-performance site-to-site connectivity. Connect all your locations securely and efficiently.
- Secure Web Gateway (SWG)
Consistent web protection and threat blocking across all sites. Control which sites and categories users can access.
- Endpoint Detection & Response (EDR)
Real-time detection on every device at every site. Ransomware and malicious files are stopped before they spread to other locations.
- Firewall as a Service (FWaaS)
Cloud firewalling for every location, without a box in each server room. One set of identity-aware rules for all sites.
Traditional Multi-Location Security vs Jimber
- Traditional
- Hardware at each site (€3K-10K+)
- Weeks per location
- Separate firewall consoles
- Broad VPN access
- Manual policy updates
- Lateral movement possible
- Jimber
- Cloud-managed, flexible controllers
- Hours to operational
- One unified console
- Granular, per-app access
- Instant deployment everywhere
- Micro-segmentation blocks spread
What this means for your organisation
After implementing Jimber’s multi-location security platform, organizations experience a fundamental shift in how security operates.
IT teams spend less time on configuration, more time on strategy. Security becomes an enabler for growth rather than a bottleneck.
Compliance becomes continuous, not a scramble. When incidents occur, containment is automatic. And security complexity stops growing with your organization.
Secure Multiple Locations the Simple Way
Stop managing separate firewalls for every location. Jimber’s Real SASE platform delivers Zero Trust security across all your sites from one console.
FAQs about Multiple Location Security
How quickly can SASE be deployed across multiple locations?
Deployment is fast because our SASE solution is cloud-native and hardware-independent. Virtual controllers can be installed in hours. Most organizations complete a full rollout across all locations within 2-4 weeks, typically with minimal to zero downtime by using a phased approach.
Do we need new hardware for every branch office?
No. Our SASE platform is hardware-independent and 100% cloud-native. For most office environments, virtual controllers are all that is required. We do offer optional physical appliances for specific use cases, such as high-throughput sites or industrial OT environments.
How does this solution work for remote users and hybrid work?
The SASE architecture is built for the hybrid workforce. Remote users are treated with the same Zero Trust policy as on-premise users. They authenticate once via our platform and get secure, granular access only to the applications they are authorized for, regardless of their location. This completely replaces the need for clunky, per-site VPN connections.
Can SASE secure temporary locations (pop-up stores, construction sites)?
Yes, this is a major advantage of a cloud-native SASE platform. Because no physical hardware is required, a virtual controller can be deployed instantly for pop-up stores, seasonal facilities, or temporary sites. They get the full, consistent security policy from day one.
How does this SASE solution help with NIS2 compliance?
Our platform directly addresses key NIS2 requirements. We provide centralized management and logging, strict identity-based access control (Zero Trust), and default micro-segmentation to limit the blast radius of any incident. This delivers the ‘least privilege’ access and complete audit trails required by the directive.
How do you secure agentless devices like printers, IoT sensors, or OT equipment?
For devices that cannot run a software agent, such as printers, IoT sensors, or industrial equipment, we use our Network Isolation Access Controller (NIAC). This appliance acts as a gateway, securing and segmenting all traffic from these devices according to your central Zero Trust policy, eliminating security blind spots.