
Managed Service Provider
Deliver Security Services Without the Chaos
One multi-tenant platform serves all your customers securely. Complete control over access, web security, and network connectivity without tool sprawl.
- 89% of MSPs struggle with tool integration
- 3 weeks to deploy
- 1 platform
The Managed Service Provider Challenge
MSPs recognize that security is their fastest growth opportunity. But delivering it profitably proves harder than expected.
- Managing 50+ clients across separate consoles creates constant context switching
- Alert fatigue hits 56% of MSP teams daily or weekly
- Five to ten different security tools multiply support burden
- Unpredictable vendor pricing erodes already thin margins
- Customer onboarding takes weeks instead of days
- VPN troubleshooting consumes billable hours without adding value
The result? Tool sprawl becomes the problem instead of the solution.
Multi-Tenant Control
One console serves every customer. Central policy templates and unified visibility eliminate console fatigue.
Predictable Economics
Transparent per-user pricing and clear margin structure. No bandwidth surprises or hidden add-on costs.
Fast Customer Wins
Three-week deployment and standardized security baselines. Onboard customers quickly without custom builds.
Real SASE for Your
Managed Security Practice
Jimber delivers complete SASE in one multi-tenant platform designed for partners. Manage all customers through one console with transparent pricing.
Five Components, One MSP Platform
- ZTNA Network Isolation
Replace VPN tickets with per-app access. Every user connects only to what they need, nothing more.
- Secure Web Gateway (SWG)
Block threats and enforce web policies across customers. Central rules apply consistently everywhere.
- SD-WAN
Connect customer sites securely without MPLS costs. Reliable links with failover and unified policy.
- Endpoint Detection & Response (EDR)
Stop ransomware on every customer device from the same console. Threats are blocked on the endpoint, with alerts per customer instead of per tool.
- Firewall as a Service (FWaaS)
One cloud firewall template for all customer sites. Roll out rules in minutes, without shipping or maintaining boxes on site.
Traditional MSP vs. Jimber
- Traditional MSP Stack
- 7-10 separate security tools
- Context switching across consoles
- Unpredictable vendor costs
- Custom builds per customer
- Weeks of onboarding complexity
- VPN support drain
- Jimber for MSPs
- One unified platform
- Single multi-tenant interface
- Transparent per-user pricing
- Standardized security templates
- Three-week deployment standard
- Self-service ZTNA access
What this means for your MSP business
After implementing Jimber’s MSP platform, service providers experience a fundamental shift in how managed security operates.
Support tickets drop as VPN troubleshooting disappears. Customer onboarding accelerates from weeks to days. Margins become predictable with transparent per-user pricing.
Technical staff focus on strategic work instead of console switching. And customer retention strengthens through consistent delivery.
Scale Your Security Practice the Simple Way
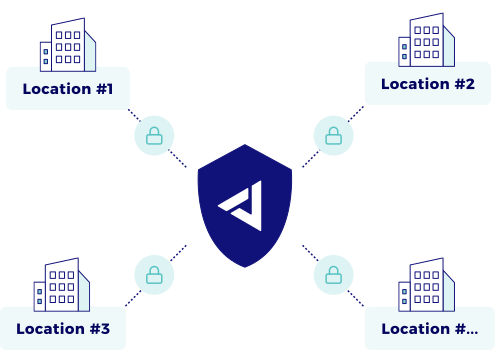
One platform, many customers, predictable growth. Jimber makes managed SASE services profitable and repeatable.
Frequently Asked Questions
How does multi-tenant management work for MSPs?
Jimber provides a single console where you manage all customer environments separately yet consistently. Each customer receives isolated policies, user directories, and reporting while you maintain central visibility across your entire client base through one interface.
The platform supports standardized security templates you can deploy repeatedly, reducing onboarding time from weeks to days. API-first architecture enables automation for customer provisioning, policy updates, and compliance reporting without manual console work for each client.
Can we maintain our existing pricing model with Jimber?
Yes. Jimber’s transparent per-user licensing adapts to various MSP pricing strategies whether you charge per device, per user, or fixed monthly fees. Our partner margin structure is clear and consistent, letting you build predictable revenue without bandwidth surprises or hidden add-ons.
Many MSPs bundle Jimber’s complete SASE platform into tiered service packages, offering basic access control at entry level and full ZTNA, SWG, SD-WAN protection at premium tiers. This flexibility helps you meet different customer budgets while maintaining healthy margins.
How quickly can we deploy Jimber for a new customer?
Most MSPs complete customer deployment in three weeks from kickoff to production. The process includes identity provider integration, application publishing for ZTNA, web security baseline configuration, and network controller placement where needed.
Standardized templates accelerate this timeline significantly. Once you’ve deployed several customers, subsequent onboarding often completes in less than two weeks as you reuse proven patterns. The unified platform eliminates the integration complexity that makes traditional SASE rollouts drag on for months.
Do we need to replace existing infrastructure to use Jimber?
No. Jimber works alongside existing firewalls, network equipment, and identity systems. Most MSPs phase in gradually, starting with ZTNA for remote access while keeping current VPN infrastructure running parallel during transition periods.
The platform integrates with major identity providers like Active Directory, Azure AD, and Okta. Network controllers can be virtual, physical, or industrial depending on customer environments. This flexibility means you can deploy Jimber where it delivers immediate value without forced infrastructure replacement.
How does Jimber handle agentless devices across customer sites?
Jimber’s NIAC hardware provides inline isolation for devices that cannot run agents like printers, IoT sensors, industrial equipment, and legacy systems. Place NIAC appliances at customer sites to create secure micro-segments for agentless equipment.
Each device or device class receives explicit access policies defining allowed communication paths. This eliminates the common security blind spot where unmanaged devices sit on flat networks vulnerable to lateral movement. Your customers get Zero Trust coverage for their entire environment, not just managed endpoints.
What compliance requirements does Jimber support for European MSPs?
Jimber aligns with NIS2, GDPR, and DORA requirements common across European markets. The platform provides centralized logging, policy versioning, and access governance features that auditors expect when reviewing managed security services.
As a Belgian company operating under European data protection standards, Jimber understands regional compliance obligations. Identity-based access control, device posture verification, and comprehensive audit trails help you demonstrate least privilege and proportionate security controls across your customer base.