
Industrial OT Security
Secure Your Production Without Shutting It Down
One cloud-managed platform bridges IT and OT securely. Complete control over industrial systems, agentless devices, and production networks: from SCADA to shop floor machinery.
- 87% ransomware spike in manufacturing
- 3 weeks to deploy
- 1 secure IT-OT bridge
The Industrial OT Security Challenge
Organizations recognize that production environments are prime ransomware targets, but traditional IT security doesn’t fit operational technology.
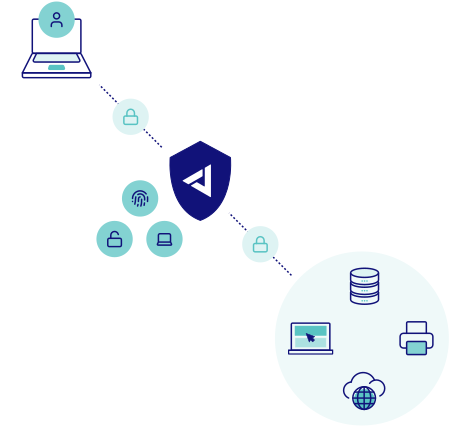
- Production systems can’t be patched without downtime
- PLCs and SCADA run on legacy, unpatched software
- Industrial devices can’t run security agents
- IT/OT convergence creates new attack paths
- Flat networks allow lateral movement to critical systems
- Regulatory pressure from NIS2 demands demonstrable controls
The result? Once attackers breach your IT network, they pivot to production systems and halt operations.
Safe Production Access
Operators authenticate once to reach HMIs and control systems. No VPN bottlenecks. No broad access risks.
Agentless Protection
NIAC hardware secures PLCs, sensors, and legacy systems. Only authorized protocols. Attacks stop early.
Secure IT-OT Bridge
Controllers create secure zones between corporate and production networks. Policies enforce least privilege.
Real OT Security
for Your Organization
Five Components, One OT Security Platform
- ZTNA Network Isolation
Operators access specific HMIs and control systems, not entire production networks. Every industrial session isolated and verified. Manufacturing uptime protected by design.
- Secure Web Gateway (SWG)
Block command-and-control traffic before it reaches shop floor systems. Industrial protocols protected. Data exfiltration from production environments prevented.
- SD-WAN
Connect multiple production sites with consistent security policies. Reliable site-to-site connectivity maintains production coordination without exposing control systems.
- Endpoint Detection & Response (EDR)
Protect the engineering workstations and HMI PCs that can reach your controllers. Ransomware is stopped on the device before it can spread to the shop floor.
- Firewall as a Service (FWaaS)
One cloud-managed firewall policy for every plant. Only approved traffic crosses between office, production and the internet, without extra boxes on site.
Traditional Industrial OT Security vs. Jimber
- Traditional
- VPN gives network-wide access
- Can’t patch without downtime
- Industrial devices unprotected
- Flat OT networks
- IT tools can’t see OT
- Air gaps don’t stop convergence
- Jimber
- ZTNA limits access per HMI/PLC
- Secure without system updates
- NIAC isolates agentless equipment
- Microsegmentation contains breaches
- Unified visibility across IT and OT
- Secure bridge between environments
What this means for your organisation
After implementing Jimber’s industrial OT platform, organizations experience a fundamental shift in production environment protection.
Production stays online. Security improves without downtime windows. IT breaches can’t reach production. Attacks stop at the boundary. Compliance becomes demonstrable, not scrambled.
When incidents occur, containment is automatic. And production security no longer requires system shutdowns.
Secure Industrial Operations the Simple Way
Stop letting IT security tools fail at OT protection. Start bridging IT and OT with purpose-built controls that respect production constraints. Jimber’s platform delivers industrial security from one console.
Frequently Asked Questions
What makes OT security different from IT security?
OT security prioritizes availability and physical safety over data protection. Industrial systems run 24/7 with near-zero tolerance for downtime: a stopped production line costs thousands per minute.
Traditional IT approaches don’t work because you can’t patch PLCs during production, install agents on 1990s SCADA systems, or reboot controllers when machinery must run continuously. The CIA triad inverts: availability first, then integrity, then confidentiality.
Jimber secures OT without touching production systems. NIAC hardware protects agentless equipment inline. Identity controls limit access per system. Zero Trust applies without operational disruption.
How do you secure devices that can’t run agents like PLCs and SCADA?
Jimber’s NIAC (Network Isolation Access Controller) sits between agentless devices and your network, creating a secure gateway without modifying industrial equipment.
When a PLC or SCADA system needs to communicate, NIAC validates against central policies and permits only authorized protocols and destinations. A PLC might send data to one historian and receive commands from one HMI, nothing more. This prevents lateral movement.
NIAC works for all agentless devices: legacy controllers, building automation, IoT sensors, and specialized machinery. Policies manage both IT and OT from one console.
Can this be deployed without shutting down production?
Yes. Implementation starts with virtual controllers handling IT-side access, so no production changes are needed. Users authenticate through ZTNA while production runs normally.
NIAC appliances deploy during planned maintenance or in monitor mode first. Industrial controllers roll out per production line: secure one line, validate, then replicate to others on your schedule.
Most organizations complete rollout in 2-4 weeks with zero unplanned downtime. Cloud-managed policies update centrally without touching PLCs or SCADA systems.
Do we need to replace our existing OT security tools?
No. Jimber complements existing investments. Industrial firewalls and OT monitoring tools keep working; Jimber fills the gaps.
Your perimeter firewalls stay for north-south traffic. Jimber adds identity-based access control and microsegmentation to stop lateral movement. OT monitoring tools become more effective when Jimber’s unified logging feeds your SIEM.
The goal is closing gaps that traditional tools miss: unprotected access paths, agentless devices, and the IT-OT boundary where convergence creates risk.
What about environments with both modern and legacy industrial systems?
Most manufacturers run modern lines alongside 1980s equipment. Jimber handles both without forced modernization.
Modern systems with agent support get full ZTNA with device posture checks and continuous monitoring. Legacy systems, such as PLCs on Windows XP and proprietary controllers, get NIAC inline protection without any system changes.
One console manages both with consistent policies. Operators authenticate once for access to modern HMIs and legacy PLCs. When you eventually modernize, only policies adjust: no architecture changes needed.
Can small and mid-sized manufacturers adopt this approach?
Absolutely. Jimber targets organizations with 50-400 employees facing enterprise threats without enterprise resources.
Cloud-managed architecture means no infrastructure to build. Virtual controllers deploy quickly. Many mid-market manufacturers work through MSPs who serve multiple clients from one multi-tenant console.
Transparent per-user pricing makes budgeting simple. One ransomware incident (11 days downtime, potential million-euro demand) proves the ROI. The platform scales seamlessly: what protects 50 users today protects 500 tomorrow without architecture changes.