
VPN alternative
Get reliable & secure network access from anywhere
Our Zero Trust Network Isolation is easier to install, more affordable and much faster & safer than traditional VPN systems.
- Fast and secure network access from any location
- Simplified setup, scalability and management
- Affordable for businesses of any size
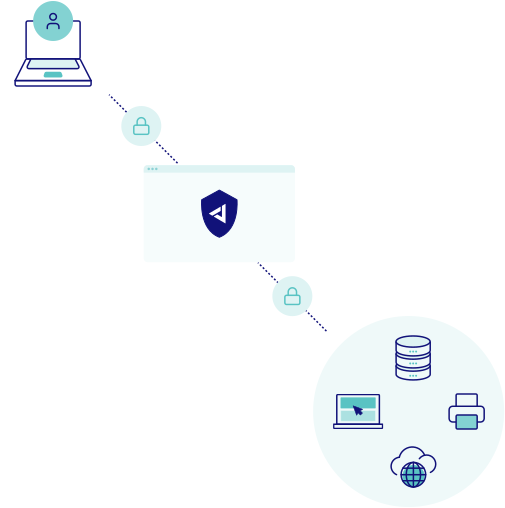
The problems with VPNs
Apart from the costly, complex and time-consuming installation of VPN systems, this security measure just isn’t optimised for today’s world anymore. If a hacker is able to bypass a traditional VPN, they get broad network access and thus full control over your company’s sensitive data.
- Constant network issues
- Needs to be combined with firewalls
- No granular access controls
- Slow connection causing latency
- Big risk of misconfigurations
- No microsegmentation of your network
The result? If you’re not upgrading your cybersecurity, hackers will come after you sooner rather than later.
Never trust, always verify
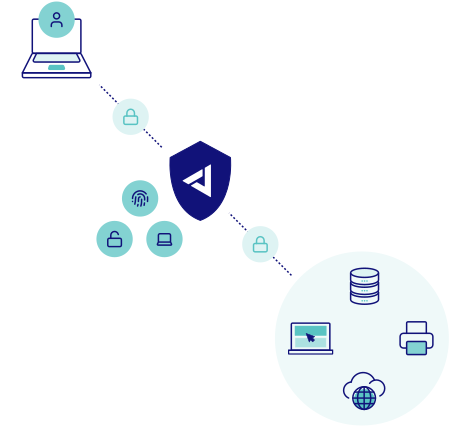
Every access request verifies the user’s identity and access rights, based on their role and responsibilities.
Micro-segmentation
Once access is granted, the user or device is isolated in its own segment, so a compromise can’t spread to the rest of the network.
One central platform
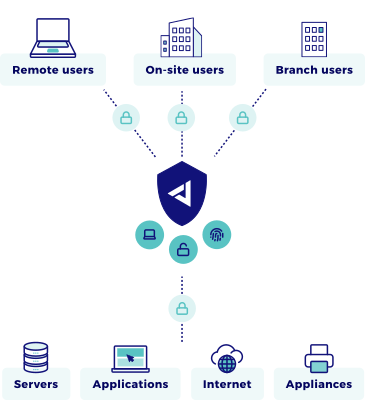
No hardware or on-premise installations: secure, manage and monitor your whole network from one place, also for remote staff and multiple locations.
Zero Trust
Network Isolation
How it works: a combination of zero trust architecture and cloud-native network isolation.
Five Components, One Zero Trust Platform
- ZTNA Network Isolation
Replace VPN’s all-or-nothing access with application-specific permissions. Every connection isolated. No lateral movement possible.
- Secure Web Gateway (SWG)
Block threats before they reach endpoints. Zero Trust policies extend to web browsing, preventing data exfiltration and credential theft.
- SD-WAN
Zero Trust doesn’t stop at applications. Secure site-to-site connectivity with the same verify-first principles across your entire infrastructure.
- Endpoint Detection & Response (EDR)
Zero Trust checks who connects; EDR checks what runs on the device. Ransomware and malicious files are stopped before they can misuse that access.
- Firewall as a Service (FWaaS)
Identity-aware firewall rules in the cloud, the same for every user and site. Network traffic gets the same verify-first treatment as applications.
VPN vs. Jimber
- VPN
- Securely connects remote users and devices to your network
- Trust, authenticate remote users and devices
- User-based, less granular access control
- Large attack surface
- Moderate to high performance impact
- May be suitable for certain regulations, depending on configuration
- Jimber Zero Trust Network Isolation
- Securely segments your network
- Zero trust, no trust by default
- Identity-based, fine-grained access control
- Reduced attack surface
- Minimal performance impact
- Suitable for regulatory compliance
Secure your network with Zero Trust Network Isolation
Zero Trust Network Isolation is a modern security solution that doesn’t rely on hardware to keep your network safe. It doesn’t require any on-premise installations either.
Instead, your entire network can be secured, managed and monitored from one central platform, even if you have remote staff or multiple locations.
In the past 12 months, 66% of SMEs have already been threatened by a cyberattack. Where the attacks were successful, the average cost of a data leak was $2.98 million, not counting the damage to their reputation.
Find out how we can protect your business
In our demo call we’ll show you how our technology works and how it can help you secure your data from cyber threats.
Why replace your VPN with Jimber?
Easy to set up and maintain
Jimber’s cloud-native approach makes this security solution easy to scale, hardware independent and highly compatible with your current solutions.
Limited downtime
Thanks to phased deployment that doesn’t require any hardware installations, the implementation of Zero Trust Network Isolation will go by almost unnoticed.
Control from a central location
You don’t need on-premise hardware to secure each individual network. Instead, you can manage and monitor all networks from one location through the Network Isolation Portal and Network Isolation Access Controller.
Granular access control
The portal makes it easy to track which users and devices are accessing specific gateways and resources. Moreover, it allows administrators to create and edit roles and permissions without much effort.
24/7 support
Jimber offers 24/7 support for its all-in-one solution, meaning all your security questions can be handled through one point of contact.
User-based security
Secure network access is based on the user’s identity and permissions, not on their location or the device they’re using.